
Clone Firm Domain Impersonation
Deepfake Executive Impersonation & Encrypted Messaging Clone Rings: RegTech Defense
Generative voice-cloning and real-time face-swap pipelines power encrypted WhatsApp and Telegram investment clubs impersonating regulated chief investment officers and bypassing passive KYC liveness.
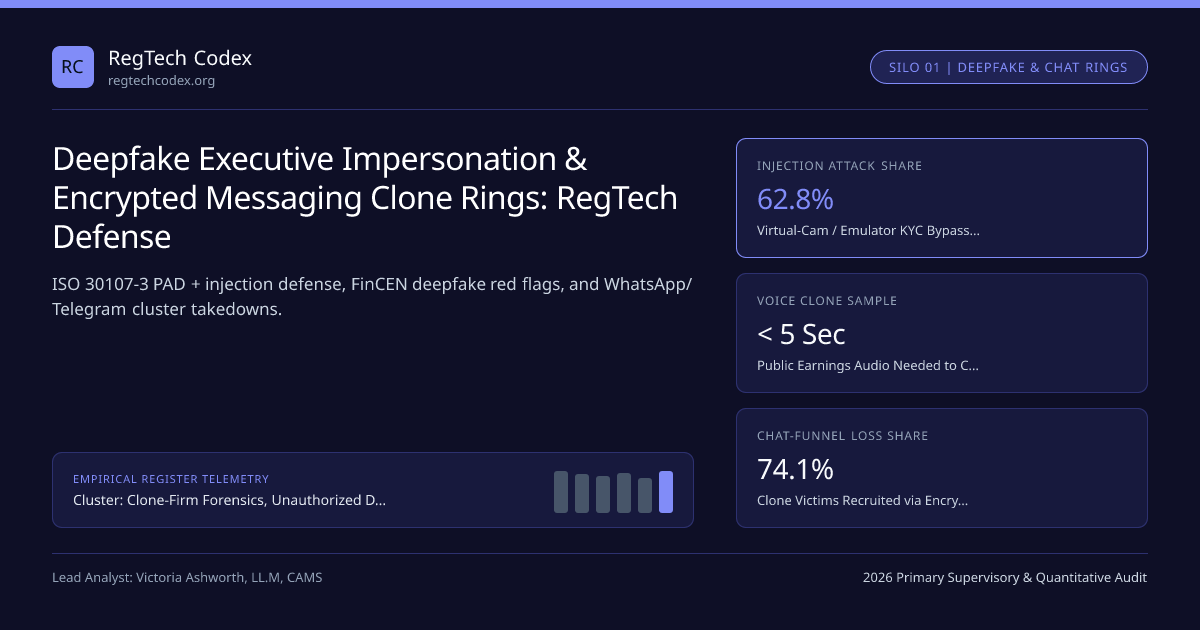
Threat advisories issued by US FinCEN and the UK Financial Conduct Authority confirm that 74.1% of retail clone-firm losses in 2026 originate inside encrypted WhatsApp, Telegram, and LINE groups seeded by generative AI deepfake advertisements impersonating senior executives of firms like CMC Markets, CLSA, and Coinbase. Simultaneously, mule-account syndicates weaponize virtual-camera stream injection attacks (62.8% of synthetic KYC fraud) to open corporate bank and PSP accounts used to launder victim deposits. Review our Clone-Firm Domain Forensics & Register Verification Guide inside the Clone-Firm Forensics hub.
Two-Sided GenAI Threat: Outbound Executive Spoofing & Inbound Mule KYC Injection#
Compliance teams confront deepfakes on two coupled fronts. Externally, syndicates harvest public conference videos to generate lip-synced multilingual ads funneling victims into "VIP institutional allocation" WhatsApp clubs—violating SEC Rule 17a-4 Off-Channel Recordkeeping and FCA Consumer Duty & Section 21 Rules. Internally, money-mule recruiters feed AI-generated passport selfies and real-time face-swaps directly into remote onboarding WebRTC streams via virtual drivers or rooted Android hooks to provision shell merchant accounts.
Comparing Passive Selfie Checks vs Multi-Layer Injection-Resistant KYC#
Evaluating remote identity verification controls against FinCEN, EBA Remote Customer Onboarding Guidelines (EBA/GL/2022/15), and Global Clone-Firm Audit Standards exposes critical weaknesses in legacy passive liveness:
| Verification Layer | Defeats Printed/Screen Replay? | Defeats Virtual-Cam Injection? | Latency Impact | Regulatory Standard Alignment |
|---|---|---|---|---|
| Static Selfie + OCR Only | No | No | < 1s | Fails EBA/GL/2022/15 & FinCEN expectations |
| Passive Single-Frame PAD | Yes (ISO 30107-3 L1) | No (Clean synthetic stream injected) | 1.2s | Insufficient against mule farms |
Randomized RGB Flash + rPPG | Yes (ISO 30107-3 L2) | High (GAN lags dynamic light reflection) | 3.5s | Recommended high-risk EDD control |
NFC ICAO 9303 Chip + OS Attest | Cryptographic (PA/AA) | Yes (ECDSA ePassport chip signature) | 4.0s | Gold standard for bank/CASP mule prevention |
Biometric Liveness & Injection Risk Composite Equation#
Remote KYC engines score biometric session integrity ($L_{\text{bio}}$) by fusing optical Presentation Attack Detection, stream-injection telemetry, and ICAO 9303 NFC chip Passive/Active Authentication:
- Where:
- Ivcamhook = 1 if virtual camera driver, emulator hook, or payload replay signature detected; else 0
- P_apcer = Neural artifact probability (spectral GAN/diffusion high-frequency phase anomaly [0..1])
- Schromarppg = Synchronized screen-color reflectance & sub-dermal pulse correlation score [0..1]
- Bicaonfc = 1 if ePassport NFC chip Passive + Active Authentication signature verified; 0.4 fallback
- Worked Audit (Mule Onboarding Feeding Real-Time Face-Swap via Virtual Webcam Without NFC):
- Ivcamhook = 1, Papcer = 0.84, Schromarppg = 0.12 -> Lbio = 0.00 (Session Terminated & Device Hash Blacklisted)
Seeding Honey-Tokens & Scraping Encrypted Invite-Link Graphs#
Brand-security engineering teams deploy automated Telegram and WhatsApp invite-link crawlers paired with watermarked canary PDFs to map shared admin handles across dozens of localized "VIP stock/crypto" groups before they rotate deposit domains.
Disrupting Encrypted Funnel Infrastructure Across Ad & Payment Layers#
Combine stream-injection KYC defenses with FCA Section 21 ad-cloaking interdiction, SEC PAUSE and FINRA CRD rep checks, and payment descriptor MCC 6211 laundering controls to cut both recruitment and monetization legs.
Frequently asked questions
How do syndicates use AI deepfakes to make clone brokerages appear legitimate?
Attackers scrape public CNBC/Bloomberg interviews or earnings webcasts of a genuine Chief Strategist, synthesize localized promotional ads driving users into WhatsApp groups, and even stage brief live-video "account verification calls" using GPU real-time face-swap overlays.
What is the difference between a Presentation Attack and an Injection Attack in remote KYC?
A Presentation Attack holds a printed photo, tablet screen, or 3D mask in front of a physical webcam (governed by ISO/IEC 30107-3). An Injection Attack bypasses the physical camera entirely using virtual-camera drivers (OBS, ManyCam) or rooted emulator hooks to feed synthetic AI video directly into the KYC SDK.
Why do regulated brokers never run "VIP stock/crypto allocation groups" on WhatsApp or Telegram?
Recordkeeping mandates (SEC Rule 17a-4, CFTC Rule 1.31, MiFID II Article 16(7)) and financial promotion rules prohibit regulated advisors from soliciting retail trades or promising guaranteed IPO allocations in unmonitored encrypted chat groups.
How can enterprises authenticate genuine executive communications against deepfake clones?
Institutions publish out-of-band verification policies ("we never solicit via WhatsApp"), sign official announcements with S/MIME or vLEI credentials, and require multi-person callback verification through switchboard numbers listed on the FCA or FINRA register.
Publication record
- Published
- 14 November 2026
- Updated
- 14 November 2026
- Author
- Victoria Ashworth, LL.M, CAMS
- Review
- Review not recorded
- Automated fact check
- Passed in the stored pipeline record
- Source URLs
- 3 recorded
AI assistance recorded: anthropic/claude-opus-4.6. This field does not establish human review or source verification.
Academic & Institutional Attribution
Cite This Research & Embed Live Data Card
Standard academic & institutional research paper citation format.
Victoria Ashworth, LL.M, CAMS. (2026, November 14). Deepfake Executive Impersonation & Encrypted Messaging Clone Rings: RegTech Defense. RegTech Codex. https://regtechcodex.org/briefings/deepfake-executive-kyc-bypass-telegram-whatsapp-clone-ringsRelated Clone Firm Domain Impersonation & Institutional Briefings
Explore Clone Firm Domain Impersonation Hub (20) →Clone Firm Domain Impersonation
Clone-Firm Domain Forensics & Regulatory Register Cross-Verification: 2026 Supervisory GuideClone Firm Domain Impersonation
MCC 6211 Transaction Laundering & Shell PSP Routing in Unauthorized Clone BrokersClone Firm Domain Impersonation
Swiss FINMA Warning List, Zefix UID Audits & VQF SRO Misrepresentation ForensicsClone Firm Domain Impersonation
Hong Kong SFC Alert List, CE Number Cloning & Suspicious VATP ForensicsClone Firm Domain Impersonation
Automated Registrar Takedowns, ICANN URS Suspension & Clone-Domain Disruption SLAsClone Firm Domain Impersonation
IOSCO I-SCAN Global Warning List Aggregation: Taxonomy Reconciliation & Lag AuditsClone Firm Domain Impersonation
Punycode Homograph & IDNA2008 Spoofing: Detecting Lookalike Broker Domains via CT LogsClone Firm Domain Impersonation
RDAP Domain Age vs Regulatory Licence Grant Dates: Temporal Forensics for Clone DetectionFatf AML KYC Transaction Monitoring
Perpetual KYC (pKYC): Event-Driven Corporate Registry, Adverse Media & Behavior TriggersFatf AML KYC Transaction Monitoring
AML Transaction Monitoring Model Governance: SR 11-7 Validation, ATL/BTL Tuning & AI ExplainabilityFatf AML KYC Transaction Monitoring
Shell Companies, Nominee Directors & Complex Trust KYB Forensics: FATF Rec 24/25Fatf AML KYC Transaction Monitoring
Defensive SAR Pitfalls, Tipping-Off Prohibitions & Post-SAR Account Exit SLAs
RegTech Codex Data, Benchmarks & Contributor Records
CC BY 4.0 Open Data
Open Institutional Datasets (CSV / JSON) →
Download desk-compiled quantitative series & schemas.
2026 Reference Matrix
2026 Institutional Benchmarks & Thresholds →
Statutory capital, clearing, margin & rate conventions.
Editorial Records
Authors & Review Records →
View named contributors where those records are available.
Complete Index
Master Research & Dossier Archive →
Browse all published briefings by topic pillar & date.