
Dora Operational Ict Compliance
NYDFS 23 NYCRR Part 500 (Second Amendment): Class A Audits, 72h Cyber & 24h Extortion Notices
New York’s Department of Financial Services enforces the strictest prescriptive cybersecurity code in the US: 23 NYCRR Part 500 Second Amendment binds NY branches, banks, and BitLicense exchanges with personal CEO + CISO certifications and 24-hour extortion alerts.
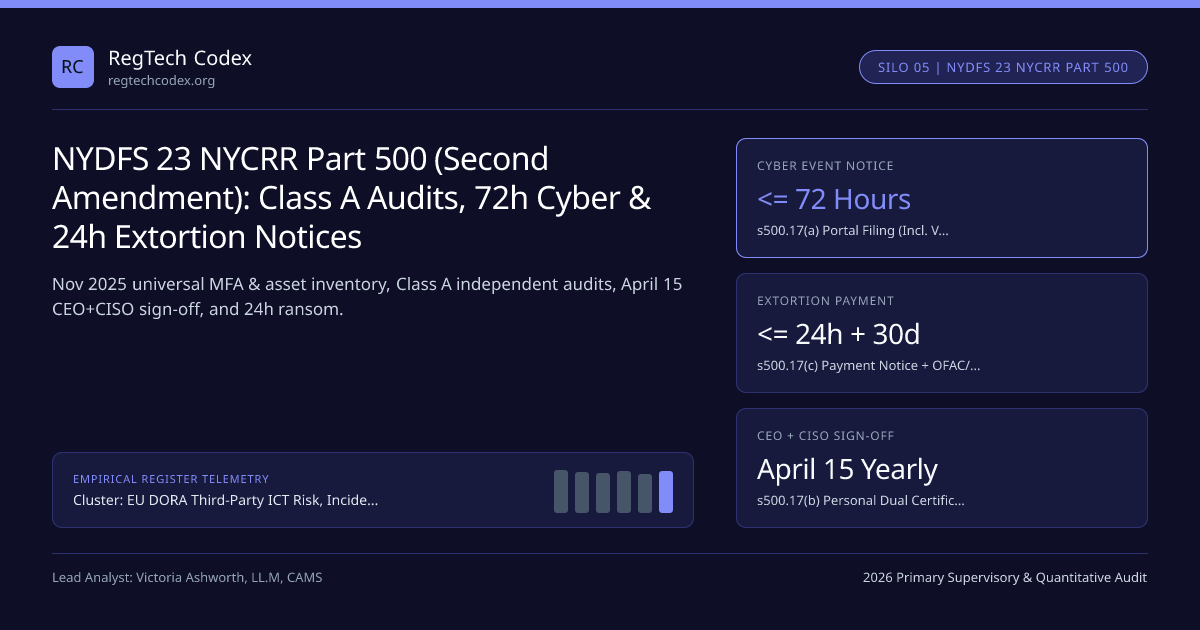
Any global bank branch, broker-dealer affiliate, money transmitter, or BitLicense virtual-currency exchange licensed by the New York State Department of Financial Services (`NYDFS`) (alongside peer state supervisors like [California DFPI](/regulators/california-department-of-financial-protection-and-innovation-218)) operates under the gold-standard enforcement hammer of US cybersecurity law: 23 NYCRR Part 500! Unlike principles-based frameworks where regulators rarely fine technical configuration gaps absent a massive breach, NYDFS has levied tens of millions of dollars in public Consent Orders (Coinbase, Robinhood Crypto, Genesis, OneMain, First American, Geico) specifically for inaccurate April 15 compliance certifications, missing MFA on legacy internal portals, and delayed 72-hour notices! Paired with EU DORA 4-Hour Incident SLAs and SEC Rule 17a-4 Immutable Evidence, firms like Coinbase and E*TRADE synchronize New York and EU cyber controls continuously. Review our EU DORA Compliance Master Guide 2026 inside the DORA operational compliance hub.
Complete 23 NYCRR Part 500 Second Amendment Control Matrix (Fully Live Post-Nov 2025!)#
Every staggered implementation deadline of the November 2023 Second Amendment—culminating in the November 1, 2025 universal MFA and Asset Inventory gate—is now active:
| Part 500 Section | Prescriptive Requirement (Active 2026) | Extra Class A Company Requirement | EU DORA Parallel | Classic NYDFS Consent-Order Trigger |
|---|---|---|---|---|
s500.12 Universal MFA (Live Nov 1, 2025!) | MFA mandatory on ALL accesses (internal LAN, VPN, cloud, SaaS, privileged & standard users!) | Block passwords lacking PAM vault; phishing-resistant FIDO2/WebAuthn preferred | RTS 2024/1774 Art. 20–21 Strong Auth | Leaving one forgotten Citrix/OWA/contractors portal on single-factor password! |
s500.13 Asset Inventory (Live Nov 1, 2025!) | Written policies + complete, tracked inventory of all hardware, OS, APIs, cloud assets (Owner, Location, Classification, Support Expiry, Recovery Time)! | Automated CMDB reconciliation tied to EDR/Vuln scanners | DORA Art. 8 + RTS Art. 4–5 ICT Asset Inventory | Decommissioned shadow servers holding live customer SSNs (Disposal breach!) |
s500.2 & 500.14 Audits, PAM & EDR | Annual risk-based pentesting + automated/manual vulnerability scans + malicious email filtering | Independent Annual Cyber Audit (s500.2(c)), PAM Vault + Password Blocker (s500.7), EDR + Central SIEM (s500.14(b))! | DORA Art. 6(6) Internal Audit + Art. 10 Detection | Counting affiliated group IT staff as "independent" without strict Audit Committee line! |
s500.17 72h / 24h / Apr 15 Filings | <=72h Cyber Event, <=24h Extortion Payment (+30d memo), Apr 15 CEO + CISO Dual Sign-Off (5-yr evidence retention)! | Same strict statutory clocks (zero weekend extensions!) | DORA Art. 19 (<=4h / <=72h / <=1m) + Art. 5 Board | Signing clean April 15 Certificate while internal Jira shows open MFA/Vuln gaps! |
Why Filing an Honest Acknowledgment of Noncompliance Beats Signing a Shaky Clean Certificate!#
Every March and April, CISOs agonize over 23 NYCRR 500.17(b) when a November acquisition or legacy mainframe migration left 3% of internal servers missing s500.12 MFA for four months of the prior calendar year. Read NYDFS Enforcement Precedents carefully: NYDFS treats signing an inaccurate Certificate of Material Compliance as an independent integrity violation carrying multi-million-dollar fines and personal career jeopardy for the CEO and CISO! That is precisely why the Second Amendment introduced the formal Acknowledgment of Noncompliance option—allowing executives to transparently identify the specific section (e.g., s500.12(a) on legacy subset X), document compensating firewalls, and commit a concrete remediation date!
Quantitative Class A Scoping & Material Compliance Sub-Certification Formula#
Group legal and finance controllers run the two-year rolling Class A Test every fiscal close and compute section-by-section Control Evidence Sufficiency:
- I( Avg2YrGlobalGroupHeadcount > 2000 OR min(GlobalGroupGrossRevY1, GlobalGroupGrossRevY2) > USD_1B )
- CanSignMaterialComplianceApr15 = prod(s in AllApplicable500Sections) I( OperatingEffectiveFullPriorYear(s) == 1 OR ApprovedCISOCompensating_Control(s) == 1 )
- > If == 0 : MUST File s500.17(b)(1)(ii) Written Acknowledgment of Noncompliance With Exact Remediation Schedule!
Watch the s500.19 Limited Exemption Trap: Even Small NY Branches Must Keep MFA & 72h Reporting!#
Foreign banks or small NY-licensed representative/money-transmitter entities qualifying for the s500.19(a) Limited Exemption (fewer than 20 employees/contractors in NY+affiliates, < $7.5M 3-year NY gross revenue, or < $15M year-end total assets) are excused from hiring a dedicated CISO (s500.4) or running continuous EDR/pentests—but they are NEVER exempt from s500.12 Universal MFA, s500.11 Third-Party Security Policy, s500.13 Data Disposal, or s500.17 72-Hour Incident / April 15 Filings!
Connecting NYDFS Part 500 to US SEC Reg S-P, EU DORA 4h SLAs & Ransomware DR#
Synchronize New York Part 500 compliance directly with US SEC Regulation S-P & Form 8-K Item 1.05 cyber rules, EU DORA Article 19 4h/72h incident clocks, and DORA Article 11–12 immutable ransomware recovery.
Frequently asked questions
What exact revenue and headcount thresholds classify a financial institution as a NYDFS "Class A Company"?
Under 23 NYCRR 500.1(d), a Covered Entity is a Class A Company if it has >=$20,000,000 in gross annual revenue in each of the last two fiscal years from NY operations (including affiliates), AND has either >2,000 employees averaged over two years globally OR >$1,000,000,000 in gross annual worldwide revenue in each of the last two fiscal years!
What changed in the annual April 15 CEO + CISO Certification under amended Section 500.17(b)?
Previously, only the Board or one Senior Officer signed attesting full compliance. Under the Second Amendment: (1) BOTH the Highest-Ranking Executive (CEO) AND the CISO must sign personally, (2) standard tightened to "material compliance" during the prior calendar year, and (3) if NOT in material compliance, they MUST file a signed Acknowledgment of Noncompliance identifying every violated section rather than filing a false clean certificate!
What did the final November 1, 2025 NYDFS Phase-In mandate on Multi-Factor Authentication (MFA, s500.12)?
Effective November 1, 2025, s500.12 eliminated old legacy internal-network exemptions: MFA is now strictly mandatory for ANY individual accessing ANY information system of a Covered Entity (whether remote or on-premises, employee or third-party!), unless the CISO approves in writing reasonably equivalent or more secure compensating controls reviewed at least annually!
What must be submitted within 24 hours and 30 days if an entity makes a ransomware extortion payment (s500.17(c))?
Under 23 NYCRR 500.17(c), a Covered Entity must electronically notify the NYDFS Superintendent within 24 hours of making an extortion payment, AND within 30 days of the payment submit a written report explaining: why payment was necessary, what alternatives to payment were considered, all diligence performed to ensure alternatives were exhausted, and all OFAC sanctions compliance diligence performed!
Publication record
- Published
- 13 November 2026
- Updated
- 14 November 2026
- Author
- Victoria Ashworth, LL.M, CAMS
- Review
- Review not recorded
- Automated fact check
- Passed in the stored pipeline record
- Source URLs
- 3 recorded
AI assistance recorded: anthropic/claude-opus-4.6. This field does not establish human review or source verification.
Academic & Institutional Attribution
Cite This Research & Embed Live Data Card
Standard academic & institutional research paper citation format.
Victoria Ashworth, LL.M, CAMS. (2026, November 14). NYDFS 23 NYCRR Part 500 (Second Amendment): Class A Audits, 72h Cyber & 24h Extortion Notices. RegTech Codex. https://regtechcodex.org/briefings/nydfs-23-nycrr-500-ciso-attestation-72h-ransom-extortion-rulesRelated Dora Operational Ict Compliance & Institutional Briefings
Explore Dora Operational Ict Compliance Hub (20) →Dora Operational Ict Compliance
EU DORA Regulation (EU) 2022/2554 Master Guide: ICT Risk, 4h/72h Reporting, RoI & TLPT (2026)Dora Operational Ict Compliance
DORA Article 45 Cyber Threat Intelligence Sharing: STIX 2.1, TAXII, MISP & GDPR/Antitrust GuardrailsDora Operational Ict Compliance
MiFID II RTS 6 Algorithmic Trading & DORA Resilience: Kill Switches, Collars & Order-to-Trade RatiosDora Operational Ict Compliance
Singapore MAS TRM & Notice PSN05/644 vs Australia APRA CPS 230: APAC Operational Resilience MapDora Operational Ict Compliance
DORA Article 5 Management Body Liability: Board ICT Training, Budgets & CISO IndependenceDora Operational Ict Compliance
DORA Article 28 & ITS (EU) 2024/2956: 15-Template xBRL-CSV Register of Information GuideDora Operational Ict Compliance
DORA Article 19 Major ICT Incident Reporting: RTS 2024/1772 Thresholds & 4h/72h/1m SLAsDora Operational Ict Compliance
DORA Article 26 Threat-Led Penetration Testing (TLPT): TIBER-EU Live Production & Purple TeamingRegulatory Compliance
Opinion | The U.K. Aims Sanctions at Israel, Hits the Cayman IslandsRegulatory Compliance
US sanctions Canadian money-exchange firms over Iran tiesMarket Insights
Here’s what happened in crypto todayRegulatory and Market Glossary
Bowman, Modernizing the Regulatory and Supervisory Landscape
RegTech Codex Data, Benchmarks & Contributor Records
CC BY 4.0 Open Data
Open Institutional Datasets (CSV / JSON) →
Download desk-compiled quantitative series & schemas.
2026 Reference Matrix
2026 Institutional Benchmarks & Thresholds →
Statutory capital, clearing, margin & rate conventions.
Editorial Records
Authors & Review Records →
View named contributors where those records are available.
Complete Index
Master Research & Dossier Archive →
Browse all published briefings by topic pillar & date.