
Dora Operational Ict Compliance
DORA Critical ICT Third-Party Providers (CTPPs): Designation Math, Lead Overseers & 1% Daily Fines
For the first time in European regulatory history, DORA Articles 31 through 44 place hyperscale cloud, market-data, and core-ledger tech giants under direct on-site inspection and penalty jurisdiction of EBA, ESMA, and EIOPA Lead Overseers.
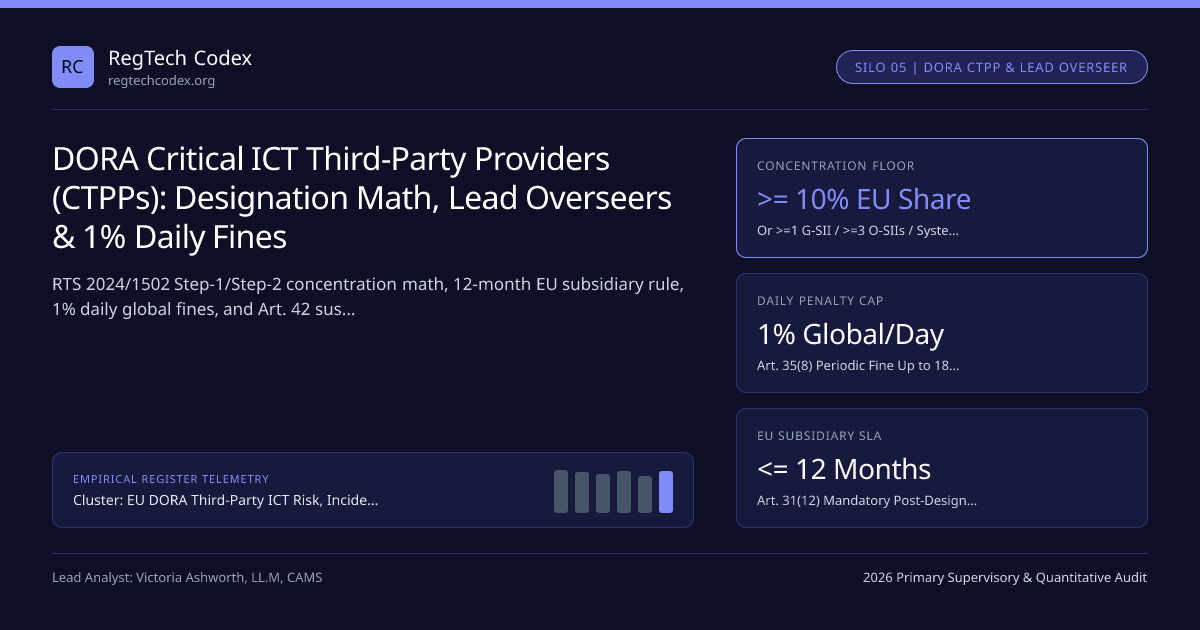
For a decade, European banks and brokerages complained of a structural asymmetry at the negotiating table: regulated firms faced strict supervisory fines if AWS, Microsoft Azure, Google Cloud, Bloomberg, or a monopolistic clearing-ledger vendor suffered an outage or blocked audit teams—yet financial regulators held zero direct legal jurisdiction over the tech giants themselves! DORA Chapter V Section II (Articles 31–44) ends that era permanently, establishing the Oversight Framework for Critical ICT Third-Party Service Providers (CTPPs) led jointly by the European Banking Authority, ESMA, and EIOPA alongside the European Central Bank under EU DORA Regulation 2022/2554 and 2026 DORA Benchmark Controls. Financial entities like CMC Markets, ICAP, Coinbase, and Anycoin Direct must understand both how their RoI filings trigger CTPP designation and what happens if an NCA invokes Article 42(6) suspension powers! Review our EU DORA Compliance Master Guide 2026 inside the DORA operational compliance hub.
Two-Step Quantitative & Qualitative CTPP Designation Funnel (Delegated Reg 2024/1502)#
A technology vendor is designated as a CTPP ONLY when it clears ALL Step-1 Quantitative Indicators across systemic impact, G-SII/O-SII reliance, and non-substitutability—followed by Step-2 Qualitative Confirmation:
Designation Criterion (Art. 31(2)) | Step-1 Quantitative Floor (Reg 2024/1502) | Step-2 Qualitative Depth Check | Data Source Feeding ESAs |
|---|---|---|---|
1. Systemic Sector Share (Art. 1–2) | Serves >= 10% of total number OR >= 10% of total asset value of EU financial entities in >= 1 DORA category (banks, venues, CASPs, insurers) | Cross-border contagion & interconnectedness across EU clearing/payment rails | Aggregated EU-wide RoI (B_01 + B_05.01 + B_06.01) |
2. Systemic Entity Reliance (Art. 3) | Supports CIFs at >= 1 G-SII, OR >= 3 O-SIIs, OR >= 1 systemic CCP/CSD/Trading Venue (or >=3 smaller systemic firms) | Intensity of real-time operational dependency on core market stability | B_01.02 G-SII/O-SII flags joined to B_06.01 CIFs |
3. Lack of Substitutability (Art. 4) | >= 10% of client financial entities report in B_07.01 either no alternative (Impossible) OR highly complex/costly migration (Difficult)! | Market concentration (nth-party Rank 2/3 cloud monopolies in B_05.02!) | RoI Table B_07.01 + B_05.02 Subcontractor Graph! |
4. Statutory Carve-Outs (Art. 31(8)) | Excludes: Regulated financial entities already under DORA, Intra-group-only ICT entities, & single-Member-State purely domestic vendors | Voluntary opt-in request permitted under Art. 31(11) | ESA Joint Oversight Forum (JOF) verification |
Why Financial Firms Must Prepare for an Article 42(6) Forced Exit Scenario!#
Look at Step 4 above—this is the single sharpest operational risk hidden inside DORA for financial-institution CTOs! Suppose a specialized US market-data or cloud middleware vendor is designated a CTPP, refuses to form an EU subsidiary under Article 31(12) (or refuses Lead Overseer cybersecurity recommendations under Article 42), and your National Competent Authority invokes Article 42(6): ordering regulated firms, as a measure of last resort, to temporarily suspend part or all of the ICT service OR terminate the contractual arrangement completely! If your firm’s Article 30 exit plan exists only on paper, an Article 42(6) order shuts down your trading desk.
Quantitative 1% Daily Global Penalty & Step-1 Concentration Equations#
Both hyperscale vendors and bank Third-Party Risk Management (TPRM) committees model the exact Reg 2024/1502 designation trigger and Art. 35(8) daily penalty ceiling:
- ShareAssets(v, cat) = SumAssetsEntitiesUsingCIF(v, cat) / TotalAssetsEUEntities(cat)
- Step1Hit(v) = I( maxcat max(ShareEntities, ShareAssets) >= 0.10 ) * I( GSIICount >= 1 OR OSIICount >= 3 ) * I( NonSub_Ratio >= 0.10 )
- DailyPenaltyCap(v) = 0.01 * ( PriorYearWorldwideConsolidatedTurnover(v) / 365 )
- Max6MonthFine(v) = 180 * DailyPenaltyCap(v) (For a $100B/yr tech giant: ~$2.74M/day -> ~$493M max!)
Pairing DORA CTPP Rules With the EU Data Act (Regulation (EU) 2023/2854) Zero-Egress Mandate!#
Compliance architects get massive commercial leverage by pairing DORA Articles 28–30 with the EU Data Act (applicable from September 2025, completely abolishing cloud-switching data-egress fees by January 2027)! Cloud hyperscalers can no longer trap regulated EU banks and brokers behind punitive petabyte egress charges during a DORA exit test.
Connecting CTPP Oversight to RoI Templates, Art. 30 Clauses & Multi-Cloud DR#
Integrate CTPP dependency tracking directly with DORA ITS 2024/2956 15-table Register of Information, DORA Article 30 contractual clauses & exit tests, and multi-cloud concentration risk & active-active RTO/RPO architectures.
Frequently asked questions
Can a US, UK, or Asian cloud/SaaS vendor with no EU corporate subsidiary be designated a DORA CTPP?
Not without establishing an EU legal subsidiary within 12 months! Under DORA Article 31(12), financial entities in the EU are STRICTLY PROHIBITED from using a Critical ICT Third-Party Service Provider established in a third country UNLESS that CTPP establishes a legal subsidiary in the European Union within 12 months following designation!
How is the EUR 500,000+ annual DORA oversight fee calculated for designated CTPPs?
Under DORA Article 43 and Commission Delegated Regulation (EU) 2024/1505, CTPPs—NOT taxpayers—fund 100% of Lead Overseer supervision costs via annual oversight fees proportional to the CTPP’s EU ICT services turnover, subject to a statutory minimum annual oversight fee of EUR 50,000!
Does a cloud provider’s designation as a DORA CTPP relieve financial firms of their own Article 28 third-party risk duties?
Never! DORA Article 31(10) and Article 28(1)(a) explicitly warn that Lead Overseer supervision of a CTPP NEVER substitutes or diminishes the financial entity’s own full legal responsibility to manage ICT risk, maintain exit plans, and test failover!
How is the 1% daily periodic penalty payment under DORA Article 35(6)-(8) calculated?
If a CTPP fails to comply with Lead Overseer information orders, investigations, or on-site inspections, the Lead Overseer can impose a daily periodic penalty payment of 1% of the CTPP’s average DAILY WORLDWIDE turnover across its preceding business year, accruing every single day for up to 6 months—AND MUST publish the fine publicly!
Publication record
- Published
- 13 November 2026
- Updated
- 14 November 2026
- Author
- Victoria Ashworth, LL.M, CAMS
- Review
- Review not recorded
- Automated fact check
- Passed in the stored pipeline record
- Source URLs
- 3 recorded
AI assistance recorded: anthropic/claude-opus-4.6. This field does not establish human review or source verification.
Academic & Institutional Attribution
Cite This Research & Embed Live Data Card
Standard academic & institutional research paper citation format.
Victoria Ashworth, LL.M, CAMS. (2026, November 14). DORA Critical ICT Third-Party Providers (CTPPs): Designation Math, Lead Overseers & 1% Daily Fines. RegTech Codex. https://regtechcodex.org/briefings/critical-ict-third-party-providers-ctpp-lead-overseer-powersRelated Dora Operational Ict Compliance & Institutional Briefings
Explore Dora Operational Ict Compliance Hub (20) →Dora Operational Ict Compliance
EU DORA Regulation (EU) 2022/2554 Master Guide: ICT Risk, 4h/72h Reporting, RoI & TLPT (2026)Dora Operational Ict Compliance
DORA Article 30 ICT Contractual Clauses: Two-Tier SaaS Repapering, Audit Rights & Exit PlansDora Operational Ict Compliance
UK Operational Resilience (FCA PS21/3 & PRA SS2/21) vs EU DORA: Cross-Mapping Dual ProgramsDora Operational Ict Compliance
US SEC Regulation S-P Amendments (2024–2026) & Form 8-K Item 1.05: 4-Day & 30-Day Cyber ClocksDora Operational Ict Compliance
DORA vs NIS2 Directive (Article 1(2) Lex Specialis): Dual-Scope Financial Groups & CSIRT SyncDora Operational Ict Compliance
DORA Subcontracting RTS (EU) 2025/532: Nth-Party ICT Supply-Chain Monitoring & Exit TriggersDora Operational Ict Compliance
AI & LLM Governance in Trade Surveillance & AML: EU AI Act (2024/1689), DORA & SR 11-7Dora Operational Ict Compliance
DORA Article 29 Cloud Concentration Risk: Multi-Region vs Multi-Cloud RTO/RPO EngineeringRegulatory Compliance
Thailand proposes $148K daily cap on stablecoin deposits and withdrawalscybersecurity
NEWS: French bank Credit Mutuel Arkea says €100m missing after cyberattack - AML IntelligenceRegulatory Compliance
After 900 IT Incidents, BaFin Expands Cybersecurity Oversight, Sets 2030 Encryption Target - Finance MagnatesRegulatory Compliance
‘Defiance’ politics risks trapping billions in capital, French regulator warns - TheBanker.com
RegTech Codex Data, Benchmarks & Contributor Records
CC BY 4.0 Open Data
Open Institutional Datasets (CSV / JSON) →
Download desk-compiled quantitative series & schemas.
2026 Reference Matrix
2026 Institutional Benchmarks & Thresholds →
Statutory capital, clearing, margin & rate conventions.
Editorial Records
Authors & Review Records →
View named contributors where those records are available.
Complete Index
Master Research & Dossier Archive →
Browse all published briefings by topic pillar & date.