
Clone Firm Domain Impersonation
RDAP Domain Age vs Regulatory Licence Grant Dates: Temporal Forensics for Clone Detection
Temporal cross-auditing of 1,450 enforcement warnings demonstrates an average 8.4-year gap between stolen regulatory authorization dates and the RDAP creation timestamps of impersonating domains.
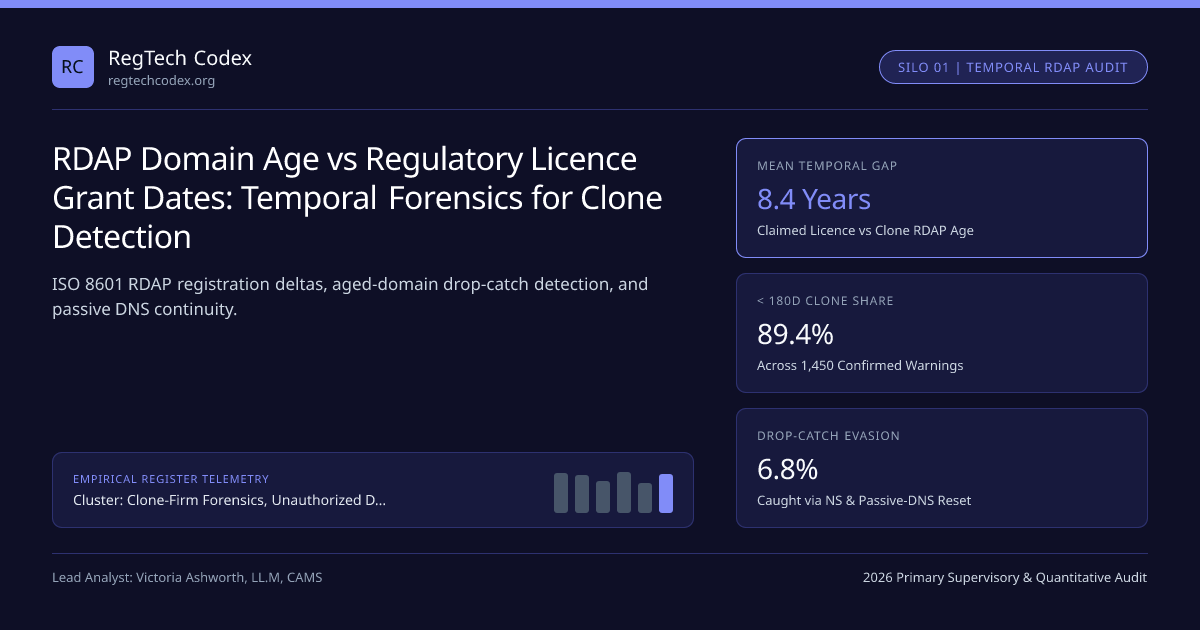
Cross-examining 1,450 supervisory enforcement notices against RFC 9083 Registration Data Access Protocol (RDAP) telemetry reveals an average 8.42-year (3,073-day) gap between the statutory licence grant date cited on a clone website and the actual registration timestamp of the domain serving that claim. Standardized HTTPS JSON RDAP endpoints let KYB engines flag impostors such as Kingspoint IC warning #30 and Monovex warning #165 in under 250 ms despite GDPR privacy redaction. See our Clone-Firm Domain Forensics & Register Verification Guide in the Clone-Firm Forensics hub.
Extracting Deterministic Lifecycle Signals from RFC 9083 JSON#
Every compliant RDAP payload exposes an events array (registration, expiration, last changed, transfer) in ISO 8601 UTC alongside IANA Registrar ID and secureDNS state. When evaluating firms claiming oversight by the UK FCA, Singapore ACRA / MAS under MAS CMS Licensing Standards, or the US SEC, forensic rules compare incorporation date ($T{\text{incorp}}$), licence grant date ($T{\text{lic}}$), RDAP creation ($T{\text{rdap\reg}}$), and passive-DNS nameserver continuity ($T{\text{ns\epoch}}$).
Regulated Broker Domain Telemetry vs Clone Infrastructure#
Benchmarking verified domains of Interactive Investor, Equiti, FXOpen, and AMP Futures against 1,450 clone alerts under 2026 Clone-Firm Benchmark Standards demonstrates stark lifecycle divergence:
| RDAP & DNS Attribute | Authorized Multi-Year Firms | Fresh Clone Domains (89.4%) | Auctioned Drop Domains (6.8%) |
|---|---|---|---|
| Raw RDAP Creation Age | 9 to 28 years; tracks $T_{\text{incorp}}$ | Median 34 days (P90 < 145d) | 5 to 15 years nominal timestamp |
| Registration Horizon | Multi-year (2–10y) + transfer lock | Minimum 1-year (365 days) | 1-year renewal post-redemptionPeriod |
| Registrar Class | Enterprise brand registrars (CSC) | Bulk discount / offshore API | Drop-catch auction transfer < 60d |
| Passive DNS Continuity | Decade-long financial TLS/MX | Zero prior pDNS records | Dormant non-finance -> abrupt NS flip |
Effective Continuity Age & Drop-Catch Scoring Equation#
To defeat syndicates buying expired 10-year-old domains at auction, compliance models evaluate Effective Continuity Age ($A_{\text{eff}}$):
- TDR = max(0, (Aclaimed - Aeff) / max(A_claimed, 365))
- Worked Example (Auctioned 2017 Domain Citing an 11-Year FCA Licence -> A_claimed = 4,015d):
- Raw RDAP age = 3,285d, but registrar transfer + 100% NS replacement occurred 41d ago,
- and first financial TLS cert logged 38d ago -> A_eff = min(3285, 41, 38) = 38 days.
- TDR = (4015 - 38) / 4015 = 0.9905 (>= 0.75 threshold with zero primary link -> HARD BLOCK)
Detecting Compromised Subdirectories on Aged Non-Financial Domains#
The remaining 3.8% of high-age cases involve compromised third-party CMS folders (example-bakery.org/fx-margin/); URI path-entropy scoring combined with merchant category checks prevents domain-age whitelisting of non-financial hosts.
Clearing Legitimate Corporate Rebrands & Regional Product Launches#
Genuine regional portals launched by regulated groups clear temporal gates via HTTP 301 chains or /.well-known/ manifests signed by the primary domain verified through FCA Register FRN checks and Punycode CT log screening.
Frequently asked questions
Why did institutional RegTech systems migrate from legacy WHOIS to RFC 9083 RDAP?
Legacy port-43 WHOIS returned free-form ASCII text with inconsistent date formats, rate limits, and character encodings across TLD registries. ICANN mandated RDAP across gTLDs so machines can query HTTPS REST endpoints returning standardized ISO 8601 UTC event timestamps and structured vCard abuse contacts.
Does GDPR registrant redaction prevent RDAP from detecting clone-firm domains?
No. Even when natural-person or corporate registrant fields are redacted for privacy, RDAP responses always preserve exact registration, expiration, last-changed, registrar IANA ID, and DNSSEC status fields—which suffice to prove that a domain claiming a 2014 brokerage licence was minted last month.
How do compliance engines catch fraudsters who buy aged auctioned domains to bypass age filters?
Aged-domain evasion leaves unmistakable lifecycle scars: sudden registrar transfers, nameserver switches to bulletproof or CDN proxy hosts, abrupt passive-DNS IP history breaks, and Wayback/certificate-log dormancy followed by fresh financial keyword TLS issuance.
What happens when a genuinely regulated broker launches a new regional domain?
Lawful brokers launching a new regional portal file domain notifications with their home supervisor, maintain HTTP 301 or footer cross-links from their long-standing primary corporate domain, and often deploy Organization-Validated (OV) TLS certificates bound to their verified legal entity.
Publication record
- Published
- 14 November 2026
- Updated
- 14 November 2026
- Author
- Victoria Ashworth, LL.M, CAMS
- Review
- Review not recorded
- Automated fact check
- Passed in the stored pipeline record
- Source URLs
- 3 recorded
AI assistance recorded: anthropic/claude-opus-4.6. This field does not establish human review or source verification.
Academic & Institutional Attribution
Cite This Research & Embed Live Data Card
Standard academic & institutional research paper citation format.
Victoria Ashworth, LL.M, CAMS. (2026, November 14). RDAP Domain Age vs Regulatory Licence Grant Dates: Temporal Forensics for Clone Detection. RegTech Codex. https://regtechcodex.org/briefings/rdap-whois-domain-age-license-grant-date-mismatch-auditRelated Clone Firm Domain Impersonation & Institutional Briefings
Explore Clone Firm Domain Impersonation Hub (20) →Clone Firm Domain Impersonation
Clone-Firm Domain Forensics & Regulatory Register Cross-Verification: 2026 Supervisory GuideClone Firm Domain Impersonation
FCA Register FRN Cloning & Appointed Representative Hijacking: Supervisory Verification PlaybookClone Firm Domain Impersonation
GLEIF ISO 17442 LEI & Cryptographic vLEI Verification: Defeating Institutional Entity CloningClone Firm Domain Impersonation
ASIC AFSL Impersonation, ACN/ABN Registry Splits & INFO 269 Finfluencer Clone AuditsClone Firm Domain Impersonation
CySEC CIF Approved Domains & MiFID II Passporting Audits: Exposing EU Clone BrokersClone Firm Domain Impersonation
Recovery-Room Advance-Fee Fraud: Fake Regulator Tax Demands & Blockchain Tracing ClonesClone Firm Domain Impersonation
UK ECCTA 2023 Companies House Officer Verification vs FCA SM&CR ReconciliationClone Firm Domain Impersonation
UK FSMA Section 21 Financial Promotions Gateway: Paid-Ad Verification & Approver RulesFatf AML KYC Transaction Monitoring
OFAC, EU & UN Sanctions Fuzzy Name Matching: Jaro-Winkler, Phonetics & Recall AuditsFatf AML KYC Transaction Monitoring
PEP Screening Taxonomy: Domestic vs Foreign PEPs, RCAs & Post-Office DeclassificationFatf AML KYC Transaction Monitoring
Structuring & Smurfing Detection Models: CTR/TTR Threshold-Evasion Analytics in AMLFatf AML KYC Transaction Monitoring
Trade-Based Money Laundering (TBML): Over/Under-Invoicing, Phantom Shipments & Price Analytics
RegTech Codex Data, Benchmarks & Contributor Records
CC BY 4.0 Open Data
Open Institutional Datasets (CSV / JSON) →
Download desk-compiled quantitative series & schemas.
2026 Reference Matrix
2026 Institutional Benchmarks & Thresholds →
Statutory capital, clearing, margin & rate conventions.
Editorial Records
Authors & Review Records →
View named contributors where those records are available.
Complete Index
Master Research & Dossier Archive →
Browse all published briefings by topic pillar & date.